French Supermarket Fridges Were Defrosted Remotely. Danfoss Says Most of the Hit Gear No Longer Gets Security Updates.
Danfoss told AFP the equipment hit was mostly legacy hardware, naming the AK-SM800 and AK-SC355. The published flaws everyone cites are in the AK-SM 8xxA series, and CISA listed them in May 2025.

By Mara Voss, Technology
· 4 min read · Updated
Key Takeaways
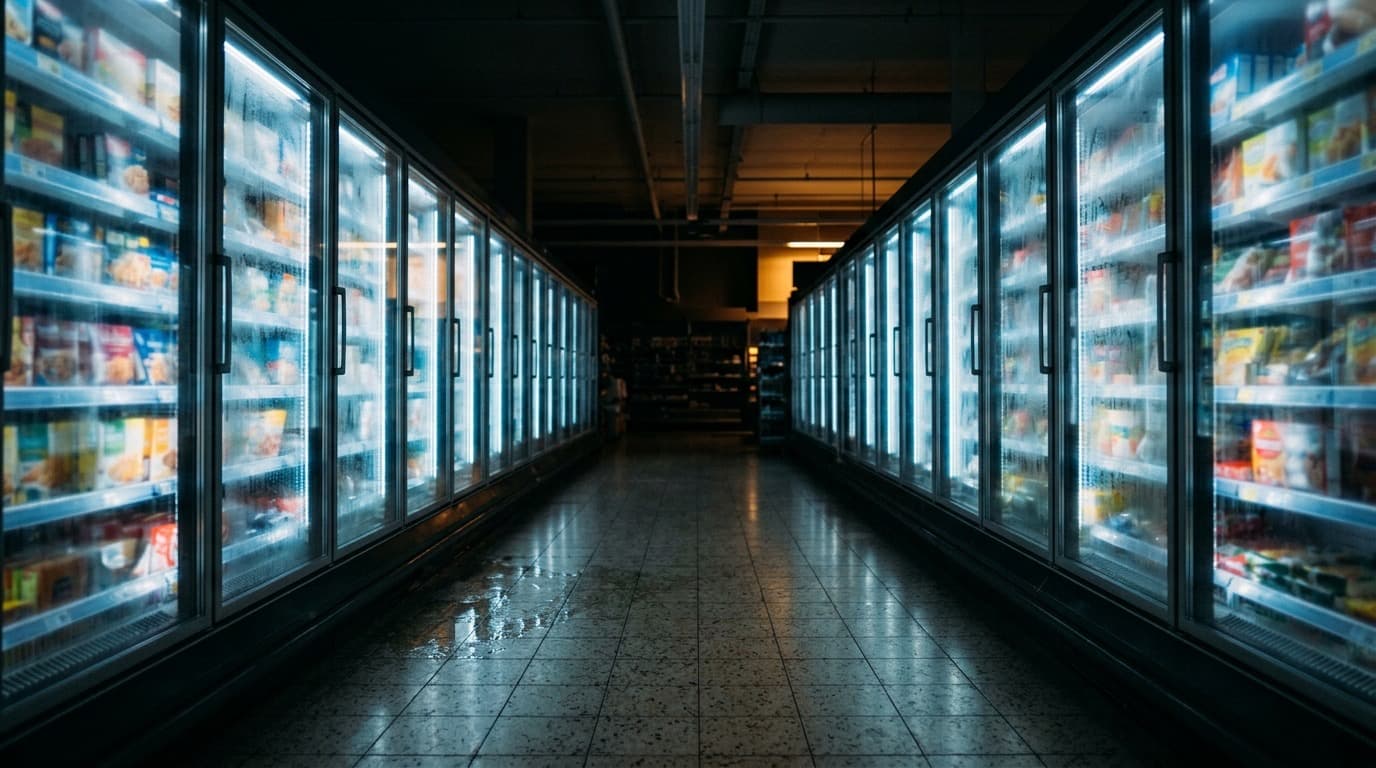
- •Attackers remotely triggered defrost on Danfoss refrigeration controllers at French supermarkets overnight on October 11 to 12, 2026, with temperatures reaching 50 degrees Celsius for about six hours, per a Mousquetaires spokesman.
- •Danfoss told AFP most affected equipment is legacy hardware that no longer receives security updates, naming the AK-SM800 and AK-SC355.
- •CISA published its Danfoss AK-SM 8xxA advisory on May 20, 2025, listing fix R4.2 for the hidden login flaw, about seventeen months before the attack.
- •Reported store counts conflict: about 150 Intermarché stores per a Mousquetaires spokesman, versus at least 300 Intermarché or Netto shops per retailer statements to AFP.
- •No report reviewed names an attacker or an entry method, or says whether any published CVE was used.
Hundreds of French supermarkets had their refrigeration sent into defrost remotely overnight on Sunday, October 11, 2026, and the controllers involved came from Danfoss. The Danish company says most of the units hit are legacy products that no longer get security updates. The firmware fix most coverage points to is for a differently named series, and the advisory behind it dates to May 2025.
The short answer
Attackers remotely triggered defrost cycles on Danfoss refrigeration controllers at French supermarkets overnight on October 11 to 12, 2026, pushing temperatures to 50 degrees Celsius. Danfoss says most affected units are legacy products without security updates, naming the AK-SM800 and AK-SC355. The flaws researchers published sit in the AK-SM 8xxA series, which CISA listed in May 2025. No report ties the attack to any specific flaw.
What the retailers say happened
A spokesman for Groupement Mousquetaires, which owns Intermarché and Netto, said fridges and freezers heated to 50 degrees Celsius, or 122 degrees Fahrenheit, for around six hours. That account comes via The Next Web. The spokesman put the Intermarché count at about 150 stores. The retailers told AFP something larger: at least 300 Intermarché or Netto shops, more than 100 Coopérative U outlets, and several E. Leclerc stores. Carrefour said 80 of its 6,000 supermarkets were hit.
Intermarché told AFP the affected branches would have to throw away all fresh and frozen products. Paris prosecutors opened an investigation and indicated the attack had also set off fires. Dominique Schelcher, chief executive of Coopérative U, called it "unprecedented" and "unacceptable" in statements reported by The Record. The retailer counts do not agree with each other, and no outlet has reconciled them.
The flaw everyone cites is older than the headlines suggest
Several reports say researchers flagged weaknesses in Danfoss controllers in August. That is the date of a write-up, not of the discovery. Claroty's Team82 published its research on August 9, 2026, but the U.S. cybersecurity agency CISA had already posted an advisory on the same family of flaws on May 20, 2025, updated August 26, 2025. It covers three CVEs in the Danfoss AK-SM 8xxA series, including a hidden "code-of-the-day" login derived from the device's date. Claroty reverse engineered the routine and wrote that anyone who could reproduce it could generate valid credentials without knowing the administrator's password.
The same advisory lists Danfoss's fixes. Release R4.2 addresses the login bypass, and R4.3.1 addresses the other two. The advisory predates this attack by about seventeen months. Claroty also counted 2,765 AK-SM 800A controllers exposed to the internet through Censys, a scan figure from the researchers, not a count of vulnerable stores.
Danfoss names different models
“no longer receive software or security updates”
Danfoss told AFP the AK-SM800 and AK-SC355 regulator systems were notably affected, with one version of the AK-SM800 running "outdated firmware." It said it had long advised supermarkets to update from those models. It gave no figure for how many systems were hit.
Read the two records side by side. CISA and Claroty describe the AK-SM 8xxA series. Danfoss names the AK-SM800 and AK-SC355. None of the sources reviewed for this story say whether those lines share code, and none says the attackers used any of the published CVEs. The Record put it flatly: it is not known whether those flaws were used.
The blame is also unsettled. Mousquetaires said Danfoss manages the affected systems and that filing a criminal complaint was the supplier's job. Danfoss says the supermarkets were told to upgrade. Both can be true, which is the problem. A person close to the French prime minister said the national cybersecurity agency ANSSI had identified "a vulnerability in software supplied by a Danish company." The source did not say which one.
Not the first time a fridge was told to defrost
In February 2019, TechCrunch reported that thousands of internet-connected industrial refrigerators from a U.K. firm, Resource Data Management, could be defrosted from a browser using default passwords found in the company's documentation. The 2019 trick needed a documented password. This one reportedly hit hundreds of stores at once.
Antoine Hautin of the consultancy Almond told AFP that refrigeration equipment long isolated from the internet is now reachable through sensors and remote monitoring. Hitting hundreds of units at once, he said, showed "a certain level of sophistication." He did not say how the attackers got in. Nobody has. As of Tuesday morning the reports reviewed for this story name no attacker, no entry method, and no list of firmware versions.
What a patch is worth here
Dutch grocer Ahold Delhaize said separately that it was dealing with a "security issue" in its network. The reports reviewed do not connect that to the French attack. The European Union's food commissioner, Christophe Hansen, said food security needs more attention at all levels.
A fix is an answer only for equipment still on a fix list. For units Danfoss calls legacy, the advice it says it gave was to move off those models, and the timing belongs to each store owner. Until someone publishes the entry point, the question is not whether a patch exists. It is whether the box on the wall can still receive one.
- Danfoss
- French supermarkets
- Intermarché
- Claroty Team82
- refrigeration cyberattack
- CISA
Sources
- 01Hackers turn up the heat in refrigerators at hundreds of supermarkets in France (AFP), October 12, 2026, CBS Newscbsnews.com
- 02Cyberattack disrupts refrigeration at hundreds of French supermarkets, October 11, 2026, The Recordtherecord.media
- 03Hackers defrost fridges at hundreds of French supermarkets, Bloomberg says, October 12, 2026, The Next Webthenextweb.com
- 04Freeze the Controller, Defrost the Food: Uncovering Vulnerabilities in Danfoss Refrigeration Controllers, August 9, 2026, Claroty Team82claroty.com
- 05ICSA-25-140-03: Danfoss AK-SM 8xxA Series (Update A), revised August 26, 2025, CISAcisa.gov
- 06Internet-connected industrial refrigerators can be remotely defrosted, thanks to default passwords, February 8, 2019, TechCrunchtechcrunch.com
Corrections
No corrections have been made to this article.
About the reporter
Technology Reporter, Trestlewire
I spent seven years as a product manager at a mid-size SaaS company before I ever wrote a sentence for pay, which means I have sat through more roadmap reviews than most people would tolerate in a lifetime. I watched a scheduling feature get rebranded three times before it shipped, and I watched a launch date slide past four straight quarters while the slide deck stayed exactly the same. That is where the question I still ask every day came from: does this actually ship, or is it a demo.
Read full bio and all stories →